Google Tag Manager (GTM) is useful precisely because I can change tags, triggers, and events without editing every application.
But I still had to maintain the initial GTM snippet in each project.
With an Astro site, WordPress, and several web apps under the same domain, that meant coordinating snippets, preventing omissions, and keeping a tracking ID in Git.
None of these tasks is particularly difficult, but they add up.
While browsing GTM, I noticed a feature called Google tag gateway for advertisers.
Its Cloudflare integration looked like a way to simplify that maintenance, so I decided to try it.
What Google tag gateway changes
Traditionally, a browser loads Google tags from Google's domains and sends supported measurement requests to Google.
Google tag gateway lets a site serve those tags and route supported requests through a path on its own domain.
For example, a configuration could use a path resembling https://example.com/metrics/...; metrics is only an illustrative path.
Google says this first-party serving approach can improve measurement signals.
That is a potential benefit, not a guarantee that every blocked request will be recovered.
It does not remove consent requirements or make ad blockers irrelevant.
Cloudflare announced its integration on May 8, 2025.
By November 2026, the feature had been available for roughly a year and a half.
Cloudflare is not the only possible integration.
Support has also expanded to providers such as Akamai, Fastly, Google Cloud, and Amazon CloudFront, and manual configurations are available for supported delivery infrastructure.
This article focuses on Cloudflare because it is already part of my setup.
The part I wanted: automatic tag injection
The especially useful option in Cloudflare's integration is automatic script injection.
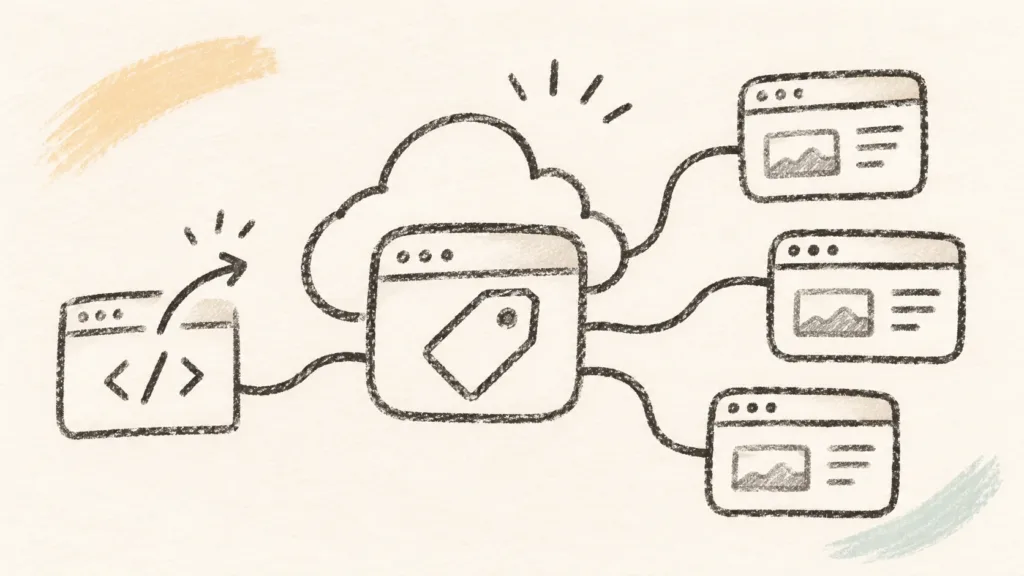
Instead of maintaining GTM installation code in each application's HTML, Cloudflare can insert the tag into responses it serves.
That gives each layer a clearer responsibility:
| Layer | Responsibility |
|---|---|
| Git repositories | Application code and application-specific events |
| Cloudflare | Gateway routing and, when enabled, tag injection |
| GTM | Tags, triggers, variables, and publishing versions |
| GA4 | Receiving and analyzing measurement events |
I can leave ordinary GTM-supported interactions to GTM and keep application-specific event notifications in application code where necessary.
This is about reducing setup work, not increasing the number of events GTM can measure.
Configuring it in Cloudflare
The site must be served through Cloudflare and use a compatible Google tag or GTM setup.
Before enabling automatic injection, identify pages you do not want to measure: WordPress admin routes, login pages, test subdomains, and similar areas.
If you use Consent Mode, also read the compatibility warning below before choosing automatic injection.
The interface varies with the setup entry point, but the process is broadly:
- Select the relevant zone in Cloudflare and find Google Tag Gateway settings.
- Connect the intended Google tag or GTM setup.
- Choose a gateway path that does not conflict with your site's existing routes. If you also want automatic GTM injection, enable the checkbox labeled “Set up tag”. Enabling the gateway alone does not inject the tag into HTML.
- Use Tag Assistant and browser developer tools to check that the expected tags and network requests appear.
- Only if automatic injection is enabled and confirmed on the target pages, remove duplicate GTM snippets from your application code.
You can also keep existing embedded GTM snippets and turn off “Set up tag” to control exactly which pages load GTM. Cloudflare's integrated setup can still route those tags through the gateway, although some manual setup methods require changing script URLs.
In the browser's Network panel, look for requests using the configured first-party path.
Check GA4 events for duplicates before and after removing older snippets.
Simply seeing the gateway active is not evidence that HTML injection is working.
UI labels and configuration options are described as of November 2026 and may change.
A zone-wide script is not a page-specific script
Automatic injection can affect pages beyond the public-facing site, including WordPress administration and test environments within the zone.
It is worth checking the actual responses for /wp-admin/, /wp-login.php, and your development hostnames.
If GTM itself must not load on certain pages, turn off “Set up tag” and keep the existing snippet only on the pages where you want it.
This can still work with the gateway; verify the first-party measurement path in Tag Assistant rather than assuming it is active.
If GTM may load but you only want to avoid sending analytics events, use a restricted Page View trigger in GTM instead of “All Page Views.”
Use built-in variables such as Page Hostname and Page Path to select production hosts and exclude unwanted paths.
Assign that trigger to the appropriate Google tag, then review the firing conditions on your other analytics tags.
Verify excluded pages with GTM Preview and GA4 DebugView.
A restricted trigger only controls tags using that trigger.
It does not stop Cloudflare from delivering the GTM container script itself.
Other tags with different triggers must be checked separately.
Cloudflare's gateway documentation describes zone-level application rather than independent subdomain switches.
Configuration Rules cannot selectively disable this automatic injection for a particular subdomain.
To prevent the script from loading on selected pages, use that existing-snippet approach rather than relying on GTM firing conditions.
Consent Mode needs special care
Google's Cloudflare setup instructions say to turn off automatic script setup when using Consent Mode.
The order in which consent defaults and tags initialize matters.
The gateway is not itself a consent banner or consent-management platform.
Cloudflare Zaraz has separate consent-related features, but those should not be confused with Google tag gateway.
Review the CMP and GTM configuration together rather than assuming that first-party delivery also handles consent.
What it does not improve automatically
Serving a Google tag on your own domain might reduce some connection overhead, but it does not remove the JavaScript executed by GTM.
Claims about improved LCP, INP, or Total Blocking Time need before-and-after measurements.
Nor does the gateway turn every third-party tag inside a GTM container into a first-party tag.
And it is not a replacement for server-side GTM, which provides a different degree of control over processing and forwarding events.
Why I adopted it
My main reason was to reduce duplicated installation code and the chances of missing or inconsistent snippets across projects.
With the application in Git, tag configuration in GTM, and delivery in Cloudflare, the responsibilities feel more manageable as the number of projects grows.
The important trade-off is scope: making GTM easier to install also makes it easier to install somewhere you did not intend.
Decide where tracking should fire—and whether the GTM script may load there at all—before enabling automatic injection.